Every consent, with a signed receipt
Each grant, withdrawal, renewal and update your customers make is kept with a signed receipt.
Your developer integrates SAMMATI once. From then on, SAMMATI keeps every consent with a signed receipt, runs your compliance portal, tells your processors when consent ends, and gives auditors proof they can verify themselves.
Your developer integrates the SAMMATI API once. From then on, SAMMATI takes care of these four things.
Each grant, withdrawal, renewal and update your customers make is kept with a signed receipt.
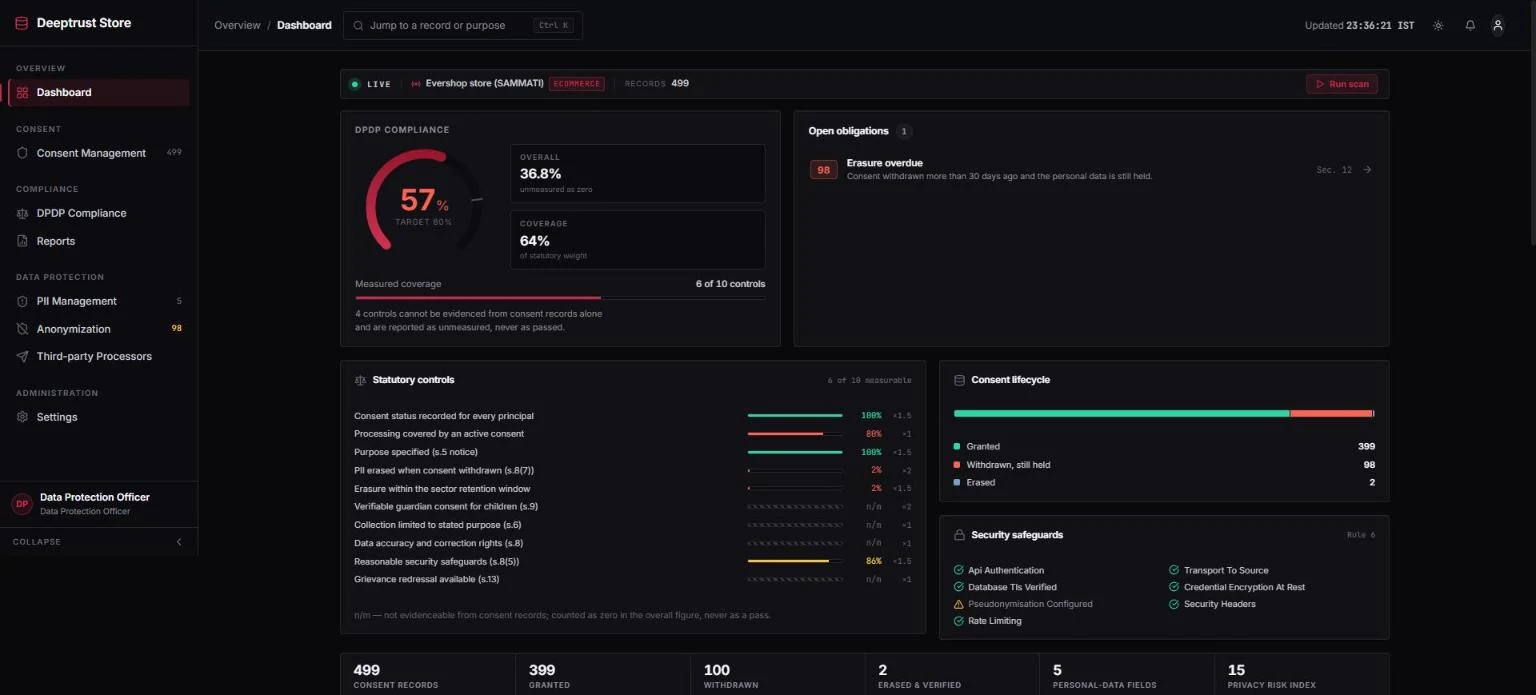
Your DPO gets a readiness score, data mapping, rights requests and the "consent ended, data still present" check.
Each processor hears by daily email, webhook or API, and acknowledges. Unanswered notices escalate after 72 hours.
Every consent's signed receipt can be checked by your auditor directly.
Your consent records and your compliance portal are one platform.
They give or withdraw consent in your app, through SAMMATI's consent calls or its hosted consent widget. SAMMATI records each decision against the notice they saw.
A collector beside your database maps where personal data sits and sends SAMMATI placeholders instead of personal data.
SAMMATI matches consent with what your systems still hold. When consent has ended but the data is still there, an erase task goes to your team; once you erase it, the collector closes the task.
Five calls: grant, withdraw, check before each use, renew and update. Or use the hosted consent widget.
SAMMATI sends your app a signed event whenever a consent changes.
A configuration file that maps your tables, with no code. It sends placeholders, never personal data.
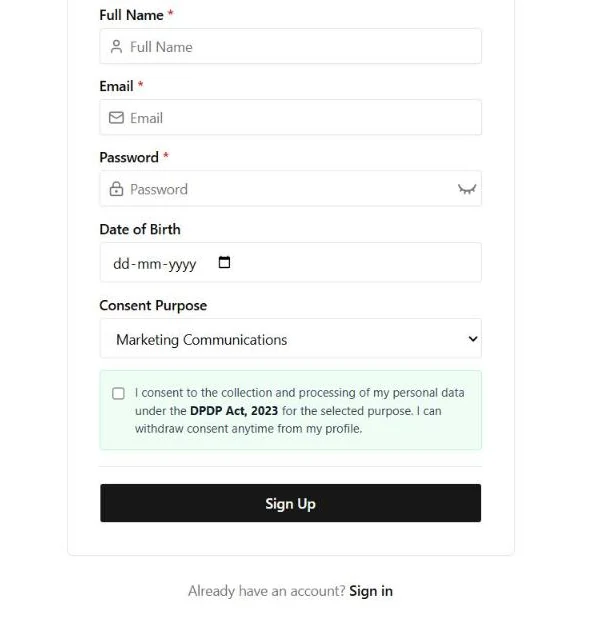
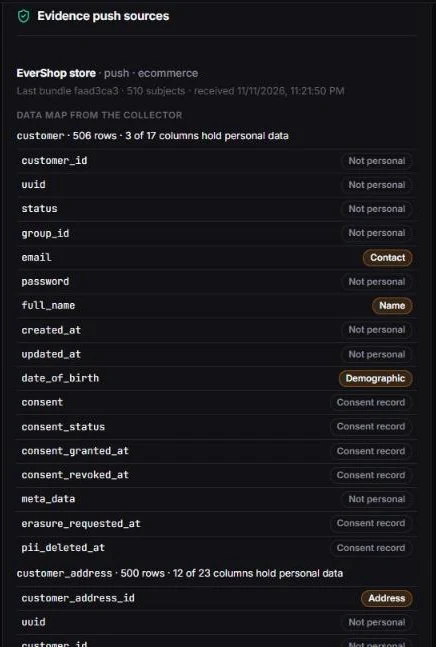
Real screens from a live store running on SAMMATI, with demo data.
Signs up, completes the company profile and publishes your purposes in Policy Studio.
Adds the consent calls or widget, one webhook endpoint and the collector.
Sees readiness, data mapping and erase tasks, and registers your processors.
By daily email, webhook or API, and acknowledge each notice.
Verify each signed receipt themselves.
Sign up, verify your email and complete the company profile
Publish your purposes in Policy Studio, as a test and a live policy
Set your allowed website and register the webhook endpoint
Build on the test key with the consent calls or the hosted widget
Set up the collector: register your database and map your tables
Switch your app to the live key
Register each processor, its purposes and how it wants to be told
After go-live, your company writes nothing more.
Sign up, pay ₹1,000 a month, and your account, keys, compliance portal space and your DPO's login are created for you.
Tell us a little about your company and we'll get in touch to set up your walkthrough.
Five consent calls in your app (or the hosted consent widget), one webhook endpoint, and a collector set up from a configuration file with no code. After go-live, your company writes nothing more.
The collector sends SAMMATI placeholders instead of personal data. That is enough for data mapping and for checking whether data is still present after consent ends.
SAMMATI records the withdrawal, tells your processors, and sends your team an erase task. Once you erase the data in your own systems, the collector closes the task.
Every consent is kept with a signed receipt, and auditors can verify each receipt themselves.
₹1,000 a month, which includes your account, keys, compliance portal space and your DPO's login.
Book a demo and we'll walk you through it on a live store.